

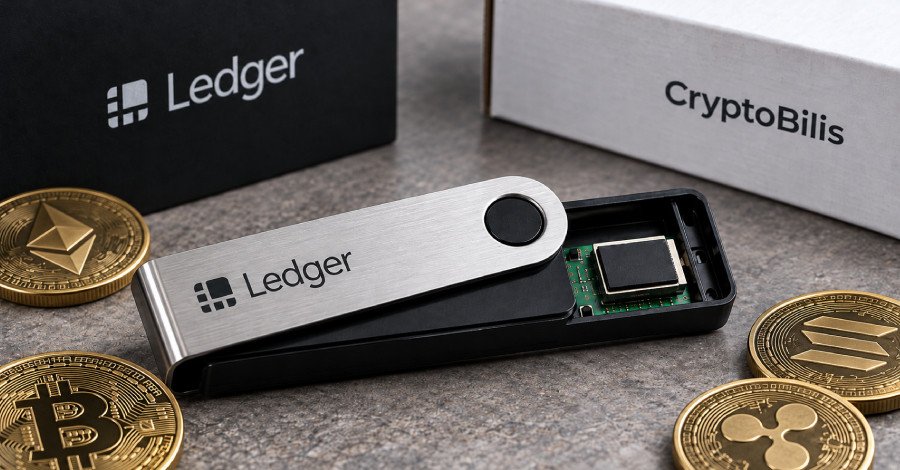

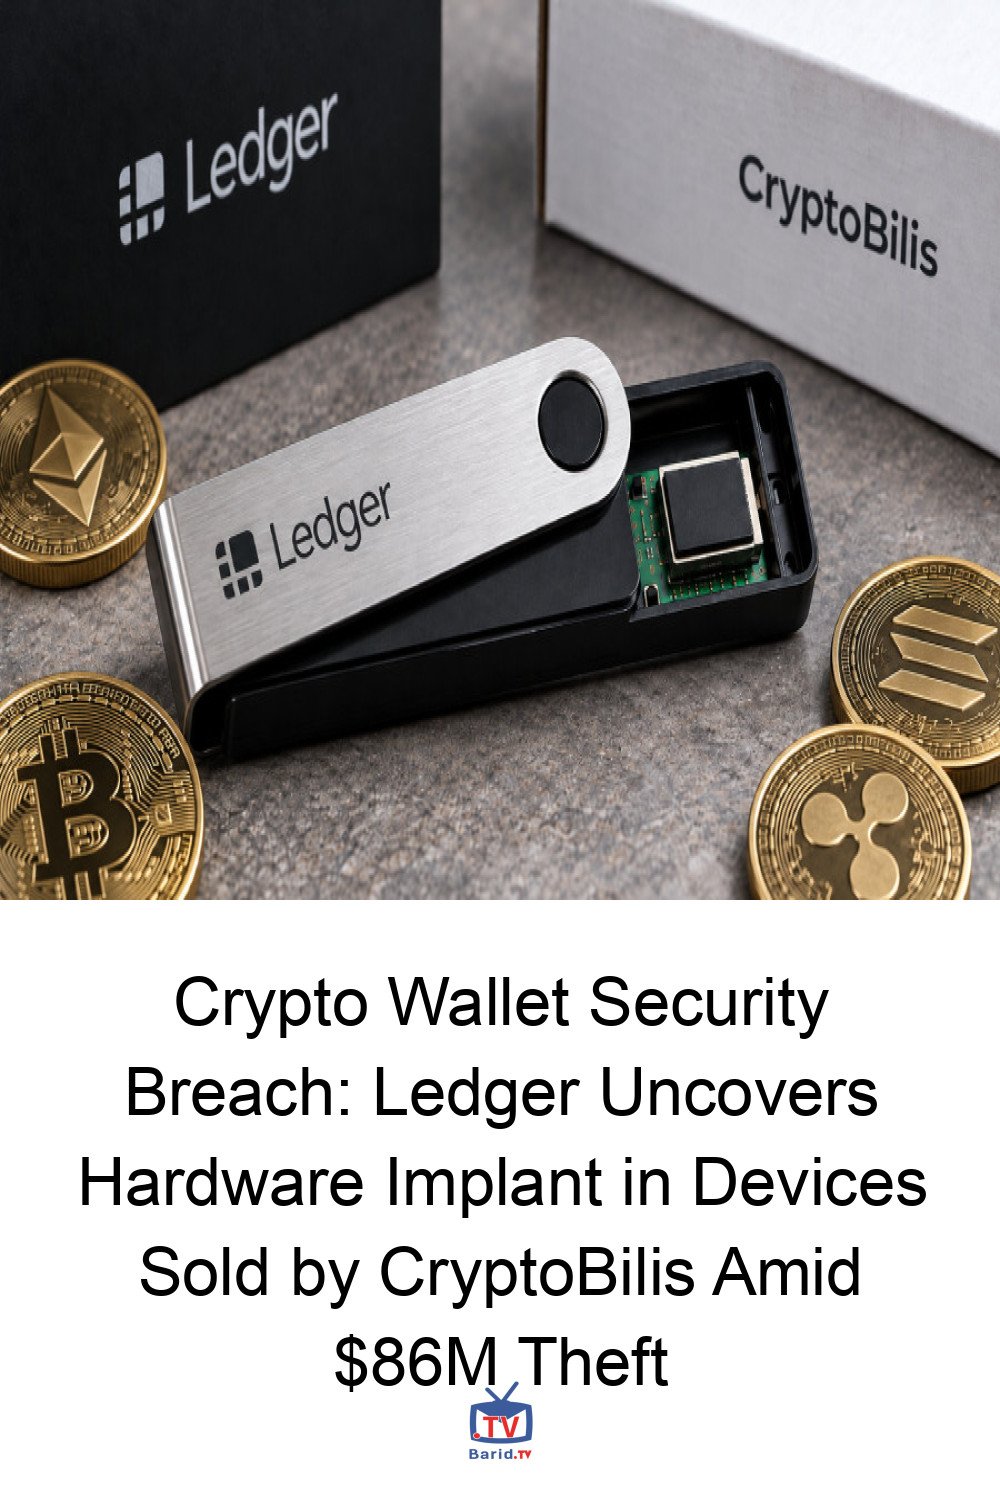
A major security alert has rocked the cryptocurrency world as hardware wallet giant Ledger has temporarily halted sales through its reseller, CryptoBilis. This decisive action follows a wave of alarming reports detailing significant fund thefts linked to devices purchased from the Southeast Asian vendor. The ongoing investigation has already unearthed a critical vulnerability: an unauthorized hardware implant discovered within one of the affected user’s devices.
Multi-Million Dollar Losses and Urgent Warnings
The scale of the alleged theft is staggering, with pseudonymous blockchain investigator Specter estimating losses exceeding a colossal $86 million. In response to these grave concerns, Ledger issued an urgent advisory to its user base:
Ledger’s Immediate Recommendations:
- For recent purchasers: “We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet.”
- For already set-up devices: “If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed).”
The discovery of a malicious hardware implant underscores the sophisticated nature of the attack and the critical need for vigilance among crypto users. Ledger has confirmed it is actively engaging with impacted users as part of its comprehensive probe.
CryptoBilis Responds: Sales Halted, Security Best Practices Reinforced
In a move reflecting extreme caution, CryptoBilis has proactively suspended all sales of its hardware wallet inventory pending the conclusion of Ledger’s investigation. The reseller has also taken the opportunity to reiterate fundamental security principles crucial for safeguarding digital assets:
Key Security Reminders from CryptoBilis:
- Recovery Phrase Generation: “Your recovery phrase must be generated by your device when you set it up, and written down by you.”
- Compromised Phrases: “If your device came with a recovery phrase already printed or written on a card or sheet, or if anyone other than you has seen your recovery phrase, treat your wallet as unsafe.”
- Confidentiality is Key: “Never share your recovery phrase or PIN with anyone. No one from CryptoBilis or Ledger will ever ask for them.”
- Beware of Scams: “Be careful of anyone who offers to recover lost funds; these offers are almost always scams.”
Ledger’s Broader Call for Supply Chain Integrity
An update from Ledger on October 11, 2026, clarified that the CryptoBilis incident has affected a “limited” number of devices, with all confirmed cases tracing back to products sold through the reseller. This incident has prompted Ledger to issue a broader warning to its entire network of resellers and distributors, emphasizing the paramount importance of supply chain integrity.
The company strongly advises against sourcing products from unauthorized channels and strictly prohibits restocking returned items without thorough verification. Furthermore, Ledger reiterated its counsel to end-users:
“Also, we strongly advise users not to purchase from unauthorized resellers, where the risk of buying suspicious, counterfeit or modified devices is important as nothing operates under ledger security guidelines.”
This evolving situation highlights the constant battle against sophisticated threats in the cryptocurrency space and the vital role of secure hardware and vigilant user practices in protecting valuable digital assets.
Stay informed on the latest developments in cryptocurrency security by following us on Google News, Twitter, and LinkedIn.
For more details, visit our website.
Source: Link


Leave a comment