


Global Cyber Espionage: FBI Uncovers China-Linked Hackers’ Email Theft & Secret Access Portal
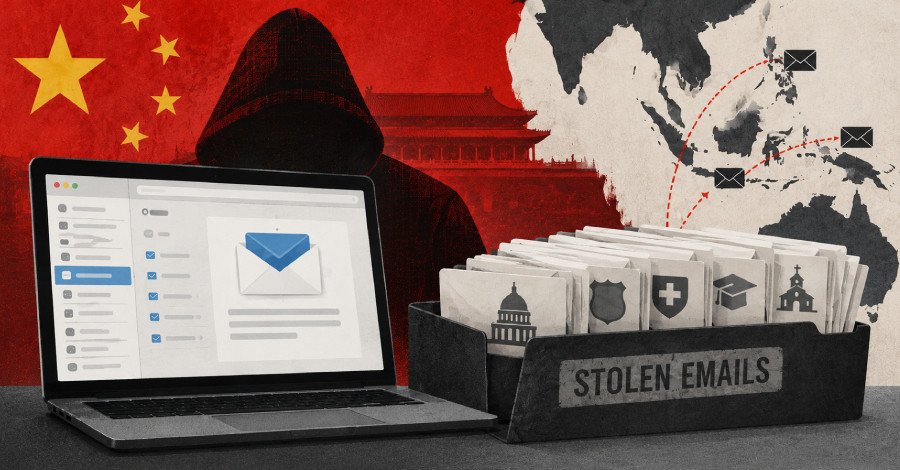
In a significant international cybersecurity alert, the Federal Bureau of Investigation (FBI) and agencies from six other nations have revealed a sophisticated, long-running cyber espionage campaign. The operation, attributed to hackers linked with China-based Integrity Technology Group, involved the theft of vast quantities of email data from sensitive targets worldwide, including government bodies, law enforcement, healthcare systems, and religious institutions. A particularly alarming discovery is the existence of a web application reportedly providing third-party access to this stolen email content.
Integrity Technology Group: A State-Linked Threat Unmasked
At the heart of this extensive cyber operation is Integrity Technology Group, a for-profit Chinese cybersecurity company described by the agencies as having direct links to the Chinese government. Its employees are alleged to develop or acquire cyber tools for both internal use and sale, establish malicious infrastructure, and actively breach networks.
The company has faced severe repercussions, with the U.S. Treasury sanctioning it in January 2025 for its involvement in multiple computer intrusions against American victims. The UK followed suit in December 2025. Former FBI Director Christopher Wray publicly stated in 2024 that the company’s chairman had openly admitted to collecting intelligence and performing reconnaissance for Chinese government security agencies for years. While the advisory uses the broad term “threat actors” for both the company and its associated hackers, the implication of state-sponsored activity is clear.
Integrity Technology Group, however, has vehemently denied the U.S. accusations, stating to the Shanghai Stock Exchange in January 2025 that the claims lacked factual basis. A Chinese Foreign Ministry spokesperson echoed this sentiment, firmly opposing the U.S. actions.
A Global Reach: Who Was Targeted?
The scope of this cyber campaign is truly global. Since at least mid-January 2021, the hackers have systematically breached networks, targeting a diverse array of organizations across continents. Victims include government services, critical manufacturing, healthcare, and IT organizations in the U.S., alongside law enforcement, educational, and religious groups. Beyond North America, organizations in Southeast Asia and Africa were also specifically targeted.
The joint advisory highlights the unique and disturbing aspect of a web application designed to offer “third-party access to stolen email content.” While the identities of these third parties remain undisclosed, the implication of a marketplace or direct sharing of sensitive intelligence is profound.
Sophisticated Infiltration Tactics
The hackers employed a multi-pronged approach to gain unauthorized access:
Vulnerability Scanning and Exploitation
Their initial reconnaissance involved scanning networks and web applications for weaknesses using both open-source tools like Nmap, masscan, and WPScan, and a proprietary Python-based scanner called MicroScan. Active since 2017, MicroScan contains over 1,300 penetration testing scripts targeting flaws in services such as OpenSSL, Oracle WebLogic Server, WordPress, and Apache Struts. The UK’s National Cyber Security Centre even noted their “uniquely using AI tools, such as automated scanning,” though the primary advisory did not explicitly mention AI.
The scans focused on common ports (21, 22, 53, 80, 443, 1080), indicating a search for readily exploitable vulnerabilities. The advisory lists several specific flaws successfully exploited, found within the hackers’ own penetration testing scripts. These include known vulnerabilities in GNU Bash, ProFTPD, ISC BIND, and Apache Struts, some dating back several years, underscoring the importance of timely patching.
Password Guessing and Mailbox Exfiltration
Beyond exploiting known flaws, the attackers also resorted to guessing passwords for Microsoft 365 and Exchange accounts. Once inside, they utilized specialized tools to copy entire mailboxes, ensuring comprehensive data exfiltration.
International Response and Disruption
This latest advisory is based on extensive evidence gathered by the FBI during multiple investigations related to Integrity Technology Group. It provides crucial insights into the hackers’ methods of infiltration and data acquisition.
In a related but distinct action in September 2024, the FBI successfully disrupted a massive botnet, dubbed “Raptor Train” by Lumen researchers. This network of over 200,000 hijacked consumer devices, including routers and cameras, was reportedly controlled by Integrity Technology Group, according to the U.S. Justice Department. While the 2024 action focused on the botnet, the current advisory sheds light on the broader cyber espionage activities and the methods used to compromise networks and steal data.
The hackers’ operational methods are consistent with those tracked by security companies under various names, including Flax Typhoon, Ethereal Panda, and RedJuliett. Microsoft, for instance, identified Flax Typhoon in 2023 as a China-based group targeting organizations in Taiwan.
The Ongoing Cyber Threat
The revelations from the FBI and its international partners serve as a stark reminder of the persistent and evolving threat of state-sponsored cyber espionage. The sophisticated tactics, global reach, and the unprecedented use of a “third-party access portal” underscore the critical need for robust cybersecurity defenses and international cooperation to counter such pervasive threats.
For more details, visit our website.
Source: Link


Leave a comment